Last updated: August 16, 2026
Quick Answer
Using consumer AI tools like ChatGPT for business work creates real data privacy risks: when employees paste client information, contracts, or internal data into a public AI platform, that content leaves your network and may be used to train the provider’s models. The risk is not theoretical. It is happening in offices across New Jersey and the country right now, often without IT’s knowledge. The fix is not banning AI. It is replacing ungoverned consumer tools with a governed platform that keeps your data isolated, logged, and under your control.
Key Takeaways
- Consumer AI tools process your data on third-party servers by default, and most free-tier accounts do not exclude your inputs from model training.
- According to Cisco’s 2025 Data Privacy Benchmark Study, 86 percent of organizations say AI is creating significant new privacy risks, yet most have not updated their data governance policies to match.
- The Cyera 2025 State of AI Data Security Report found that shadow AI use (employees using unapproved tools) is the top concern among security leaders, ahead of external attacks.
- Employees can accidentally leak sensitive data through AI tools without any malicious intent, simply by doing their jobs faster.
- Industries handling financial records, health information, or legal documents face the highest exposure.
- A governed AI platform provides the same productivity benefits as consumer tools, but with data isolation, access controls, and full audit logging.
- Any business subject to GDPR, HIPAA, or state-level privacy laws may face compliance liability from uncontrolled AI use, even without a breach.
- The difference between data privacy and data security in AI is important: privacy governs who has the right to use data, while security governs who can access it. Ungoverned AI puts both at risk.
- MacWorks 360 has supported New Jersey businesses for over 30 years. The MacWorks 360 AI services page outlines current options for deploying governed AI.
- Auditing your AI vendor before deployment is one of the highest-value steps any SMB can take this quarter.
What Are the Main Data Privacy Risks When Using AI in Business?
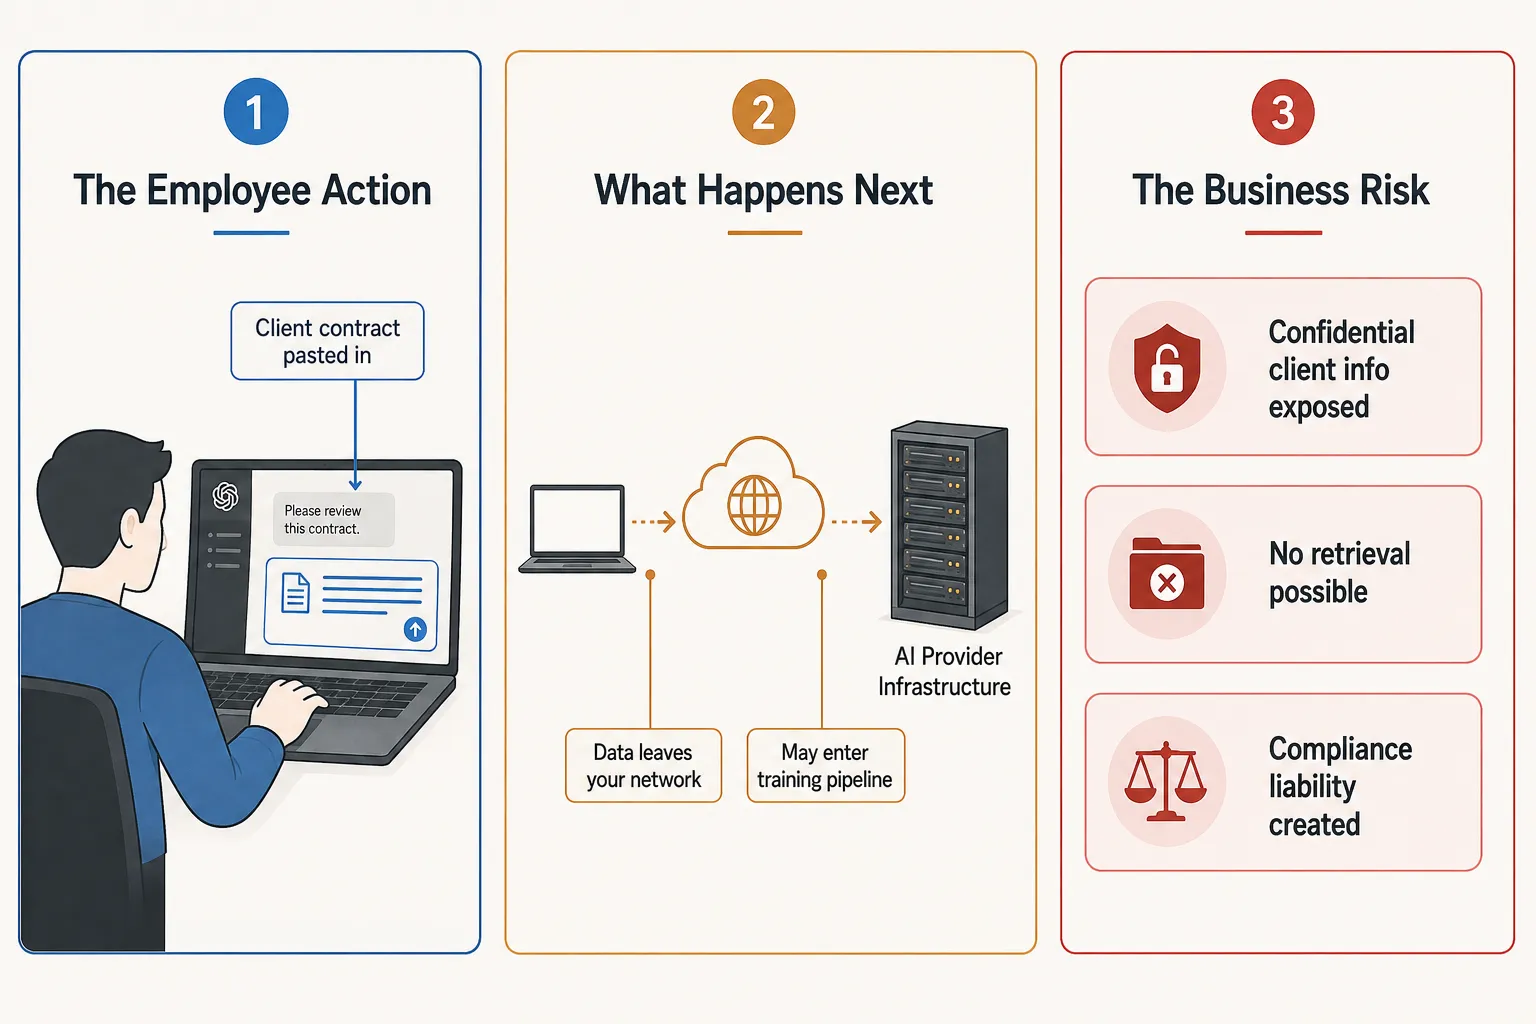
The core risk is data exposure through inputs. Every time an employee types or pastes content into a consumer AI tool, that content is transmitted to and processed on the provider’s infrastructure. Depending on the tool’s terms of service, the provider may store that content, have human trainers review it, or use it to improve future model versions.
The DataGrail AI Privacy Risks Report identifies four primary categories of AI-related privacy risk for businesses:
- Unintentional data disclosure: Employees sharing client names, financial figures, or internal strategy without realizing the data leaves the building.
- Training data exposure: Inputs being incorporated into a model that other users can indirectly query.
- Lack of data subject rights: Once data enters a third-party AI system, honoring deletion or access requests under privacy law becomes difficult or impossible.
- Opaque data flows: Most consumer AI tools do not provide the audit trails businesses need to demonstrate compliance.
For small and mid-sized businesses, the practical danger is not a dramatic breach. It is a slow, invisible accumulation of sensitive information sitting in systems outside your control, with no record of what was shared or when.
Why Is My Business Data Being Used to Train AI Models?
Most free and consumer-tier AI tools include language in their terms of service that permits them to use your inputs to improve their models. This is not hidden, but it is rarely read. Unless a business has explicitly opted out or subscribed to an enterprise tier that contractually excludes training use, the default is permissive.
OAIC guidance on generative AI tools in the workplace notes that many organizations assume their data is protected simply because they use a reputable provider. That assumption is incorrect without a formal data processing agreement.
For businesses in New Jersey, this matters practically. If a contractor uses a personal ChatGPT account to draft internal documentation, that account isn’t isolated from the provider’s training pipeline. The company’s internal processes, client names, and pricing logic may enter a dataset the business can’t see and can’t remove.
The fix is straightforward: move to a platform that contractually excludes your data from training. Enterprise tiers of major AI providers and governed platforms like Goodweek both offer this. The key is getting it in writing before your team starts using the tool, not after.
Can Employees Accidentally Leak Data Through AI Tools?
Yes, and it happens constantly. Accidental data leakage through AI tools is not a failure of intent. It is a predictable outcome of giving employees powerful productivity tools without clear policies or technical guardrails.
Three scenarios illustrate how this plays out in real business environments:
- An employee pastes a client’s personal or financial information into an AI chatbot to “clean up” a report. The data is now outside the company’s control, processed on a third-party server, and potentially retained indefinitely.
- A sales team uses an AI tool to summarize a competitive deal, including pricing, strategy, and client names. Once submitted, the company cannot recall that information. A future model update could surface patterns derived from it.
- A contractor uses a personal ChatGPT account to help write internal documentation. The free account has no data isolation. The company’s internal processes are now in someone else’s training dataset, with no audit trail and no way to verify what was captured.
The BigID AI Risk and Readiness in the Enterprise 2025 Report found that fewer than a third of organizations have implemented technical controls to prevent sensitive data from being submitted to AI tools. Policy alone, without platform-level enforcement, does not prevent these incidents.
Common mistake: Assuming that because an employee “knows better,” they will not paste sensitive content. Under time pressure, people default to the fastest tool available. Governance needs to be structural, not behavioral.
What Is the Difference Between Data Privacy and Data Security in AI?
These terms are often used interchangeably, but they describe different problems with different solutions.
Data security in AI refers to preventing unauthorized access to your data. It covers encryption, access controls, network protection, and breach prevention. A security failure means someone who should not have your data gets it.
Data privacy in AI refers to controlling how your data is collected, used, shared, and retained, even by parties authorized to process it. A privacy failure means your data is used in ways you did not consent to or cannot verify, even if no external attacker is involved.
For businesses using AI tools, both risks can occur at the same time. A consumer AI platform may be secure (no external hacker accesses it) while still creating a privacy violation (your client data trains a model you did not authorize). The ICO guidance on AI and data protection makes this distinction clearly: data protection law applies to how AI systems process personal data, not just whether they protect it from attackers.
For SMBs, the practical implication is this: vetting a vendor’s security certifications is necessary but not sufficient. You also need to review their data-use policies, retention schedules, and training-data practices.
What GDPR Violations Can Happen When Using AI?
Any business that processes personal data belonging to EU residents, or that operates under a state-level equivalent like New Jersey’s own privacy framework, can face compliance exposure from uncontrolled AI use. The violations do not require a dramatic breach. They can arise from routine use of the wrong tool.
The revised EDPS Opinion on Generative AI identifies several compliance failure points relevant to businesses using consumer AI:
- No lawful basis for processing: Submitting client personal data to an AI tool without a documented legal basis (consent, legitimate interest, or contractual necessity) violates the GDPR.
- Failure to honor data subject rights: If a client requests deletion of their data and the business has already submitted it to a third-party AI system, it may be unable to comply.
- Lack of a Data Processing Agreement (DPA): Using a third-party AI vendor without a signed DPA means the business is transferring data to an uncontrolled processor, which directly violates GDPR.
- Purpose limitation breach: Using data collected for one purpose (a client transaction) to train an AI model is a secondary use that requires separate justification.
For businesses not directly subject to GDPR, the same logic applies under emerging U.S. state privacy laws. The pattern of liability is the same: using personal data in ways the subject did not anticipate, without controls in place to prevent or document it.
Which Industries Face the Biggest AI Data Privacy Threats?
Any industry that regularly handles personal, financial, legal, or health information faces elevated risk when employees use consumer AI tools. In practice, the highest-exposure sectors for New Jersey SMBs include:
- Professional services (legal, accounting, consulting): Client files, financial records, and privileged communications are frequently the exact content employees want AI to help process.
- Healthcare and medical practices: Any use of AI that involves patient information triggers HIPAA obligations, even if the AI provider isn’t aware it is handling protected health information.
- Financial services and insurance: Regulatory requirements around data handling are strict, and the data employees work with daily (account numbers, income figures, risk assessments) is precisely what should not enter an ungoverned AI system.
- Real estate and property management: Lease agreements, tenant records, and transaction data are high-value targets and frequently processed with AI tools.
- Staffing and HR: Employee records, compensation data, and background check results are sensitive by definition.
The Kiteworks analysis of the Stanford AI Index 2025 notes that regulated industries are adopting AI at the same pace as unregulated ones, but often without the governance infrastructure to match. That gap is where liability accumulates.
What Is the Difference Between Cloud AI and On-Premise AI for Data Privacy?
Cloud AI tools (ChatGPT, Claude, Gemini, and similar) process your data on the provider’s infrastructure. Your inputs travel over the internet to external servers, are processed there, and may be retained according to the provider’s policies. The privacy risk depends entirely on the terms of service and whether a data processing agreement is in place.
On-premise AI deployment runs the model on hardware within your own network. Your data never leaves your building. This eliminates the training data risk and the third-party retention risk. The tradeoff is cost and complexity: on-premise deployment requires hardware investment, IT expertise to maintain, and typically produces less capable models than the frontier systems available through cloud providers.
A middle path, and the one most appropriate for New Jersey SMBs, is a governed cloud AI platform. Tools like Goodweek sit between the two extremes: they provide access to frontier models (GPT, Claude, Gemini) through a managed layer that contractually excludes your data from training, enforces department-level data isolation, and logs every interaction. The data still travels to a cloud environment, but under terms and controls that a consumer account never provides.
Choose on-premise if: Your regulatory environment absolutely prohibits third-party data processing, and you have the IT infrastructure to support it.
Choose a governed cloud platform if: You want frontier AI capability with enterprise-grade privacy controls, without the overhead of running your own infrastructure.
Avoid consumer cloud tools if: You handle any personal, financial, health, or legally privileged information in the normal course of business.
How Much Does It Cost to Implement AI Data Privacy Compliance?
The cost of AI data privacy compliance for an SMB depends on the approach taken, but the baseline is lower than most business owners expect. [FLAG FOR MACWORKS 360 REVIEW: Confirm current pricing ranges before publishing.]
At minimum, compliance requires three things: a governed AI platform with a contractual data processing agreement, a written internal AI use policy, and a brief staff training session. For most SMBs, the platform cost is the primary line item, and governed platforms like Goodweek are priced for business use, not enterprise budgets.
A more relevant comparison is between the platform fee and the potential liability of inaction. The Cisco 2025 Data Privacy Benchmark Study found that organizations with strong privacy programs report significantly lower costs from data incidents than those without. For a New Jersey SMB, a single client data exposure incident can carry legal fees, regulatory scrutiny, and reputational damage that far exceeds a year of platform costs.
The practical starting point is an AI tool audit (see the section below). It costs nothing except an hour of attention, and it tells you exactly what you are working with before you make any budget decision.
How Do I Know If an AI Tool Is Safe for My Customer Data?
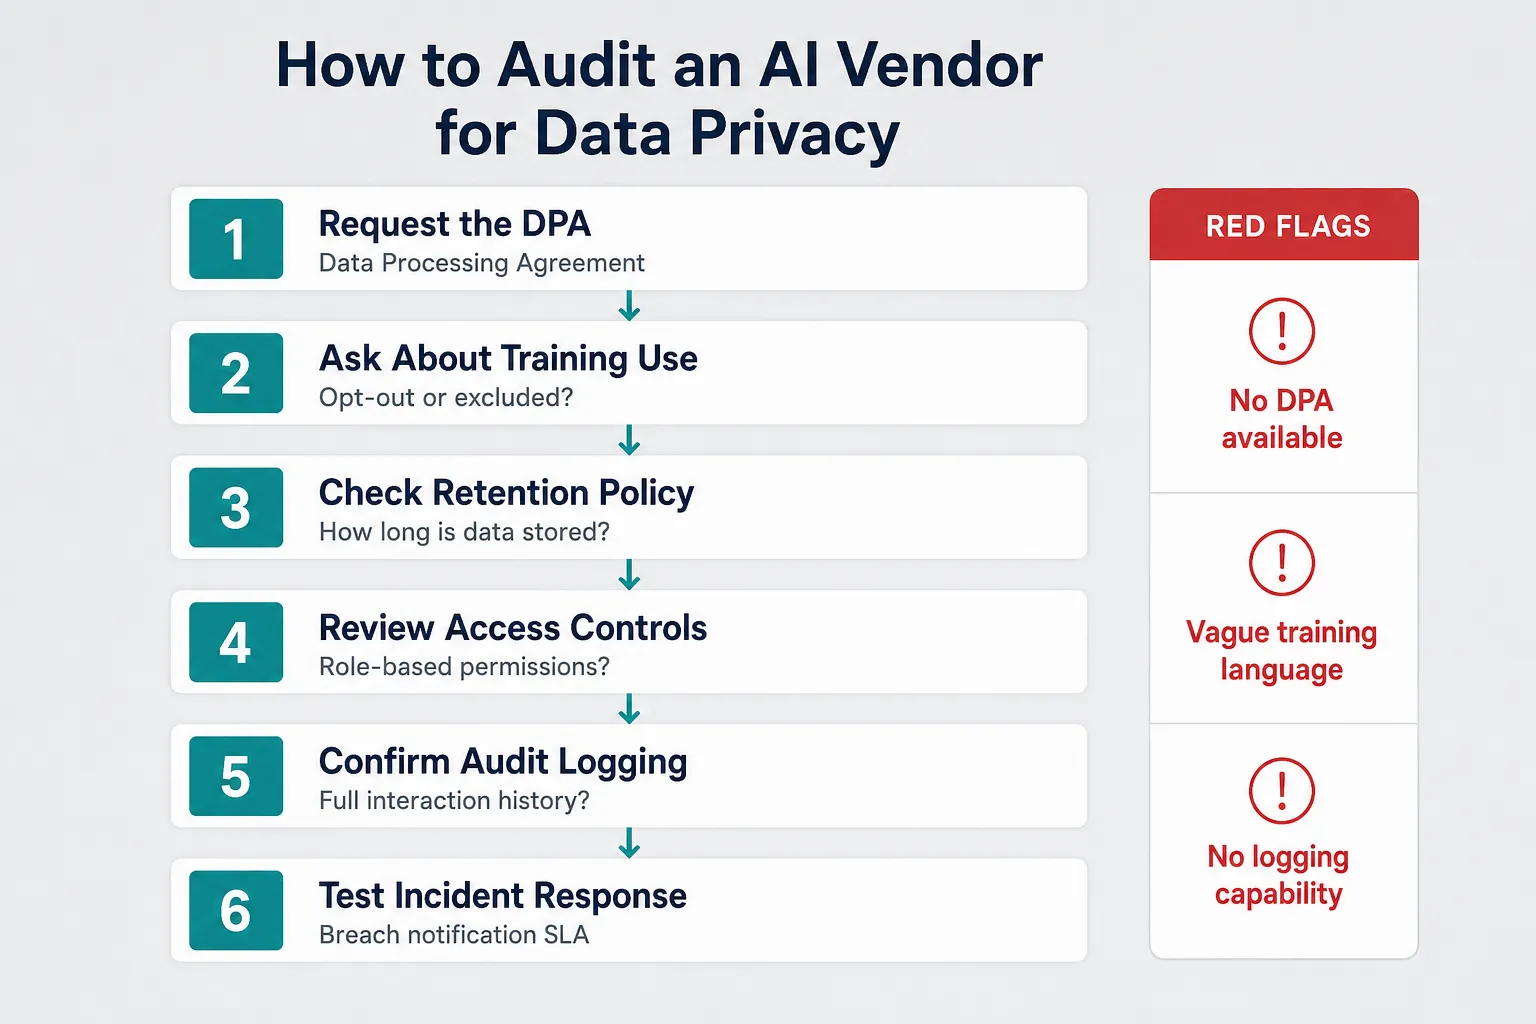
An AI tool is safe for customer data only if you can verify specific contractual and technical protections, not just trust a brand name. Here is the checklist to apply before approving any AI tool for business use:
- Request the Data Processing Agreement (DPA). If the vendor cannot provide one, stop. No DPA means no legal framework governing how your data is handled.
- Ask explicitly whether your inputs are used for model training. Get the answer in writing. “We may use data to improve our services” is not a sufficient opt-out.
- Review the data retention policy. How long does the vendor store your inputs? Is there a deletion mechanism?
- Confirm role-based access controls. Can you restrict which employees access which features and data categories?
- Verify audit logging. Can you pull a record of every AI interaction, including what was submitted and what was returned? This is essential for compliance and incident response.
- Check the incident response SLA. If a breach occurs, how quickly must the vendor notify you?
Red flags that disqualify a tool for business use: no DPA available, vague language about training use, no logging capability, and no clear data residency information.
For businesses that want help running this evaluation, MacWorks 360’s AI services include vendor assessment as part of a governed AI deployment engagement.
How to Audit an AI Vendor for Data Privacy Risks
Auditing an AI vendor is a structured process, not a one-time checkbox. For SMBs, a practical audit covers six areas:
Step 1: Documentation review. Collect the vendor’s privacy policy, terms of service, DPA, and any published security certifications. Look for specific language about training data exclusion, not just general privacy commitments.
Step 2: Data flow mapping. Identify exactly what data your team submits to the tool and what category it falls into (personal data, financial data, privileged communications)—map where that data goes after submission.
Step 3: Access control review. Confirm that the platform supports role-based permissions. A tool where every employee has identical access to all features and data categories is a governance gap.
Step 4: Logging and monitoring. Test whether the platform produces exportable logs of AI interactions. If it does not, you cannot demonstrate compliance in an audit or investigate an incident after the fact.
Step 5: Subprocessor review. Ask the vendor which third parties they share data with. AI platforms often use multiple subprocessors, each adding another data exposure point.
Step 6: Ongoing review cadence. AI vendor terms change. Schedule a review of your vendor’s policies at least annually, and any time a major product update is announced.
This process applies whether you are evaluating a new tool or reviewing tools already in use. Because shadow AI adoption is widespread, the audit should cover tools employees use independently, not just those IT has approved. Reviewing your team’s digital security habits alongside AI tool use is a natural pairing.
What Should Be in an AI Data Privacy Policy?
An AI data privacy policy for an SMB does not need to be long, but it needs to cover specific ground. A policy that says only “employees should use AI responsibly” provides no actual protection.
A functional AI data privacy policy includes:
- Approved tools list: Name the specific AI tools employees are permitted to use for work purposes. Anything not on the list requires IT approval before use.
- Prohibited data categories: Explicitly list what cannot be submitted to any AI tool: client personal information, financial records, health data, legal documents, internal pricing, and employee records.
- Account requirements: Specify that employees must use company-provisioned accounts, not personal accounts, for any work-related AI use.
- Incident reporting: Define what constitutes a reportable AI data incident and how employees should report it.
- Review schedule: Commit to reviewing the policy at least annually, given how quickly AI tool capabilities and terms of service change.
Pair the policy with a brief training session so employees understand not just the rules, but the reasons behind them. A team that understands why pasting a client contract into ChatGPT creates risk is far less likely to do it than one that has been told not to.
How Does AI Data Anonymization Actually Work?
Data anonymization in AI refers to processing or transforming data so that individuals cannot be identified from it, either directly or in combination with other available information. In practice, true anonymization is harder to achieve than most businesses assume.
Common techniques include removing direct identifiers (names, account numbers, addresses), generalizing data (replacing a specific age with an age range), and adding statistical noise to datasets. The challenge is that modern AI systems can sometimes re-identify individuals from data that appears anonymized, particularly when combined with other publicly available information.
For SMBs, the practical implication is this: anonymizing data before submitting it to an AI tool reduces risk but does not eliminate it. A better approach is to avoid submitting personal data to consumer AI tools altogether and to use governed platforms that contractually restrict what the vendor can do with inputs, whether or not they are anonymized.
The ICO guidance on AI and data protection notes that anonymization must be robust enough that re-identification is not reasonably possible, a standard that is difficult to meet with informal redaction practices.
Common Mistakes Businesses Make With AI Data Privacy
These are the patterns that create liability, not dramatic failures but routine oversights:
Assuming enterprise-grade protection from a consumer account. A business email address does not make a free ChatGPT account a business tool. The account tier determines the data handling terms, not the user’s job title.
Treating AI policy as an IT-only concern. AI data privacy risk is a business risk. It belongs in conversations with legal, HR, and department heads, not just IT.
Approving a tool once and never reviewing it again. AI vendor terms of service change. A tool that was acceptable under last year’s terms may not be acceptable today.
Relying on employee judgment without technical controls. Policy without enforcement is an aspiration. Governed platforms enforce data-handling rules at the system level, removing dependence on individual behavior under time pressure.
Not inventorying what tools are already in use. The Cyera 2025 State of AI Data Security Report found that shadow AI use is pervasive. Most businesses that have not conducted an AI tool audit underestimate how many tools their teams already use.
Conflating “no breach” with “no risk.” The absence of a known incident doesn’t mean data hasn’t been exposed. It may mean the exposure has not been detected yet.
What to Do This Week
Before making any platform decisions, start with a simple audit. These three steps take less than two hours and give you an accurate picture of your current exposure:
- Ask your team directly: What AI tools are you using for work, including personal accounts? Guarantee no-blame reporting to get honest answers.
- Review the terms of service for each tool identified: Look specifically for language about training data use and data retention. If you cannot find a clear opt-out, assume the default is permissive.
- Identify the highest-risk use cases: Where is your team submitting the most sensitive content? Client communications, financial summaries, and legal documents are the priority categories to address first.
Once you have that picture, the conversation about governed AI platforms becomes concrete, not theoretical. MacWorks 360 has spent over 30 years helping New Jersey businesses make technology decisions that hold up under scrutiny. The MacWorks 360 team is available for a straight conversation about what a governed AI setup looks like for your specific business, with no sales pressure and no obligation.
Call 973-671-1122 or request a free consultation at macworks360.com.
Also worth reviewing as part of your broader security posture: the practical guide to identifying phishing emails and the data breach password guidance on the MacWorks 360 blog. AI data privacy does not exist in isolation from your overall security practices.
Frequently Asked Questions
Is ChatGPT safe for business use?
ChatGPT’s consumer and free tiers are not designed for business data. By default, inputs may be used to improve OpenAI’s models, and there is no department-level data isolation or audit logging. The enterprise tier includes stronger protections, but requires a formal agreement and configuration. For most SMBs, a governed AI platform is a more practical and consistently protected option.
What happens to data I submit to a public AI tool?
It is transmitted to the provider’s servers, processed to generate a response, and may be retained according to the provider’s data retention policy. On free and consumer tiers, human trainers may also review it or use it to train the model. Once submitted, you cannot retrieve or delete it unilaterally.
Does using AI tools violate GDPR?
It can, depending on what data is submitted and under what terms. Submitting personal data about EU residents to a third-party AI tool without a Data Processing Agreement, a lawful basis for processing, and a mechanism to honor data subject rights can violate the GDPR, even if no breach occurs.
What is a governed AI platform?
A governed AI platform provides access to frontier AI models (such as GPT, Claude, or Gemini) through a managed layer that adds enterprise controls: data isolation between departments, contractual exclusion from model training, role-based access permissions, and full audit logging of every interaction. Goodweek is one example of this category.
How do I know if my employees are using unapproved AI tools?
Ask them directly, with a no-blame framing. Shadow AI use is widespread precisely because employees find these tools genuinely useful. A better question than “are you using AI?” is “what tools are you using to get your work done faster?” That framing surfaces the honest answer.
Can a contractor’s personal AI account expose my business data?
Yes. A contractor using a personal free-tier account to work on your projects has no data isolation from the provider’s training pipeline. Your internal processes, client names, and business logic may enter a dataset you can’t see and can’t contractually require the provider to remove.
What is the difference between a privacy policy and a data processing agreement?
A privacy policy describes how a company handles data in general terms, primarily for end users. A Data Processing Agreement (DPA) is a contract between a business and a vendor that specifies exactly how the vendor will handle the business’s data, including restrictions on training use, retention periods, and breach notification obligations. For business AI use, the DPA matters most.
Do small businesses really need to worry about AI data privacy?
Yes. Small businesses handle the same categories of sensitive data as large ones (client personal information, financial records, employee data) and face the same compliance obligations. The difference is that large enterprises typically have legal and compliance teams reviewing vendor contracts. SMBs often do not, which makes the risk of an ungoverned tool adoption higher, not lower.
How often should we review our AI tools and policies?
At minimum, annually. In practice, review whenever a major AI provider announces a product update or terms-of-service change. AI tool capabilities and data handling practices are changing faster than most annual review cycles can track.
What is the first step to securing our AI use?
Conduct an inventory. Find out which AI tools your team is currently using, including personal accounts used for work tasks. Until you know what is in use, you cannot assess the risk or make informed decisions about what to replace or govern.
References
- DataGrail. “AI Privacy Risks Report.” Help Net Security, June 2026. https://www.helpnetsecurity.com/2026/06/01/datagrail-ai-privacy-risks-report/
- Cisco. “2025 Data Privacy Benchmark Study.” Cisco Newsroom, April 2025. https://newsroom.cisco.com/c/r/newsroom/en/us/a/y2025/m04/cisco-2025-data-privacy-benchmark-study-privacy-landscape-grows-increasingly-complex-in-the-age-of-ai.html
- Cyera and Cybersecurity Insiders. “2025 State of AI Data Security Report.” Cybersecurity Insiders, 2025. https://www.cybersecurity-insiders.com/wp-content/uploads/2025-State-of-AI-Data-Security-Report-Cyera-by-CSI.pdf
- BigID. “AI Risk and Readiness in the Enterprise: 2025 Report.” BigID, 2025. https://home.bigid.com/hubfs/AI%20Risk%20%26%20Readiness%20in%20the%20Enterprise-%202025%20Report.pdf
- ICO. “Guidance on AI and Data Protection.” Information Commissioner’s Office, UK. https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/artificial-intelligence/guidance-on-ai-and-data-protection/about-this-guidance/
- OAIC. “GenAI Tools in the Workplace: Balancing Protection of Personal Information and Business Efficiency.” Office of the Australian Information Commissioner. https://www.oaic.gov.au/news/blog/GenAI-tools-in-the-workplace-balancing-protection-of-personal-information-and-business-efficiency
- DP Institute. “Revised EDPS Opinion on Generative AI.” DP Institute, 2025. https://www.dp-institute.eu/en/revised-edps-opinion-on-generative-ai/
- Kiteworks. “AI Data Privacy Wake-Up Call: Stanford AI Index 2025.” Kiteworks, 2025. https://www.kiteworks.com/cybersecurity-risk-management/ai-data-privacy-risks-stanford-index-report-2025/