Last updated: August 16, 2026
Quick Answer: Cross-department AI data leakage happens when a shared AI tool surfaces sensitive information from one team (HR, Legal, Finance) inside another team’s conversation, with no malicious action required. Because most off-the-shelf AI tools have no concept of organizational access controls, deploying one across your whole company without proper governance creates a single undifferentiated data pool that every user can inadvertently tap. The fix is a combination of isolated AI workspaces, role-based permissions, and a written internal policy that defines who can use AI for what.
Key Takeaways
- Cross-department AI data leakage occurs when a shared AI tool has no access boundaries between teams, allowing sensitive data from one department to surface in another’s queries.
- No hacking or malicious intent is required. The AI returns whatever seems relevant from everything it has been fed.
- HR, Legal, Finance, and Sales face the highest exposure because their data carries legal and professional confidentiality obligations.
- The risk is structurally different from a traditional external data breach. It is quieter, harder to detect, and often invisible until the damage is done.
- Governed AI platforms use isolated workspaces and role-based permissions to enforce departmental boundaries at the architecture level.
- Technology alone is not enough. A clear internal policy must define authorized uses, data boundaries, responsible owners, and violation procedures.
- Compliance exposure is real. Cross-contamination of certain data categories can violate GDPR, HIPAA, and other frameworks, depending on the data involved.
- Auditing AI usage across departments is now a core IT governance responsibility, not an optional extra.
- Employees can and do accidentally expose company data through AI chatbots, particularly when using general-purpose consumer tools for work tasks.
- An IT partner who understands your organizational structure is essential to designing a workspace architecture that actually matches how your business operates.
What Is Cross-Department AI Data Leakage?
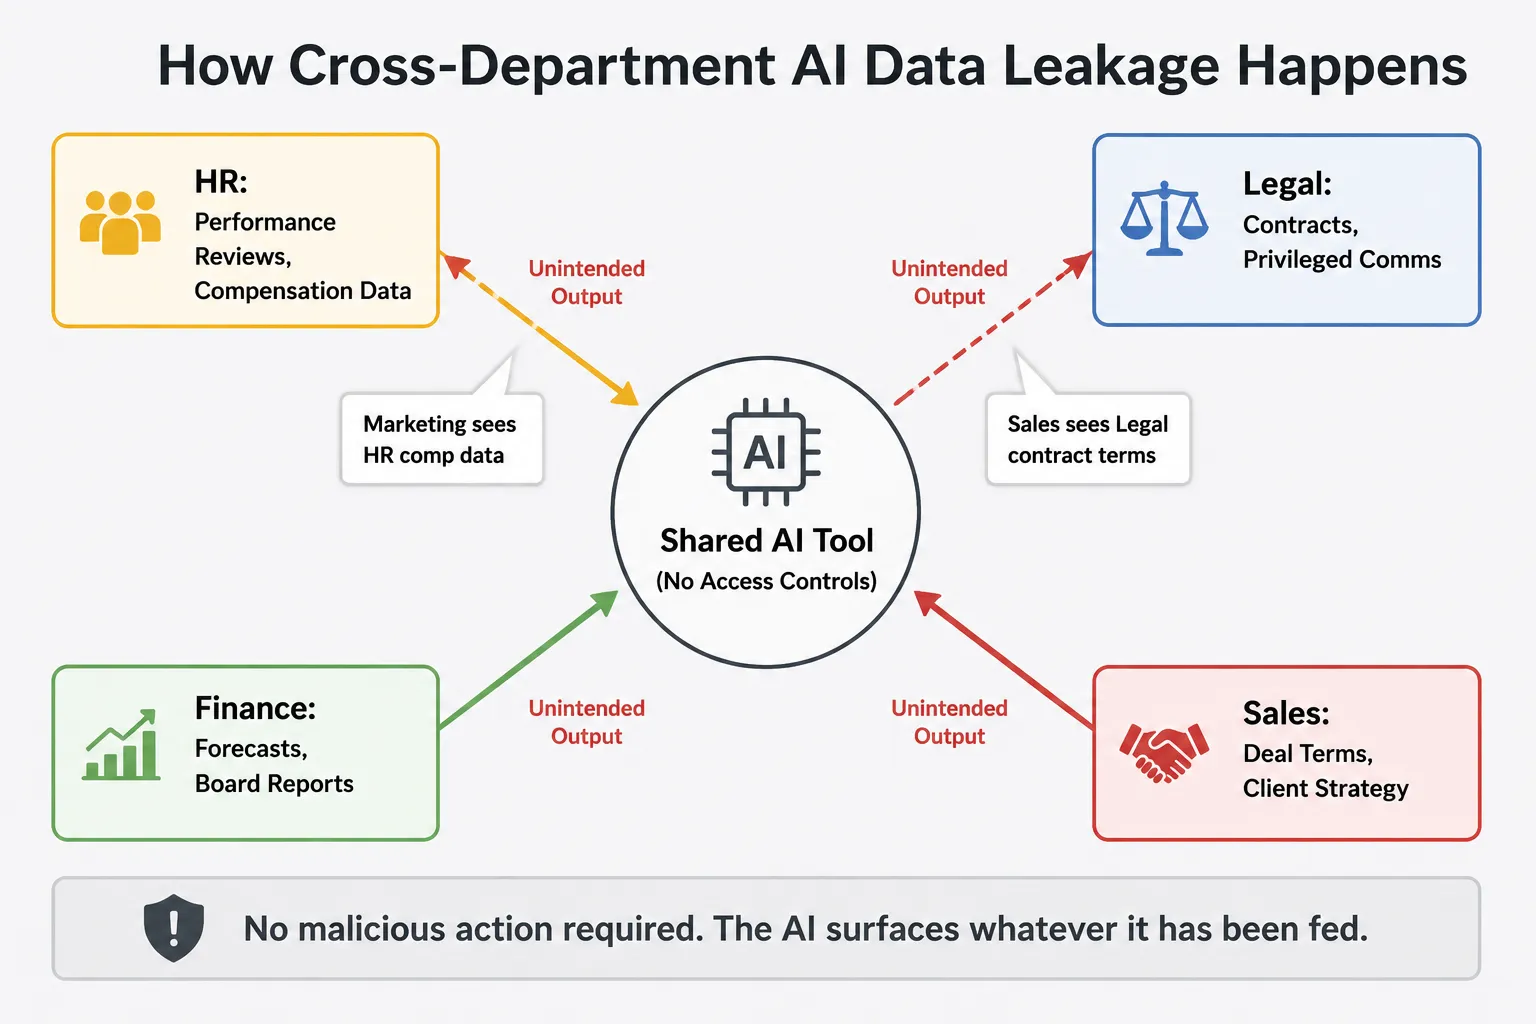
Cross-department AI data leakage is the unintended exposure of one department’s sensitive data to another department’s users through a shared AI tool. It does not require a cyberattack, a misconfigured server, or a negligent employee. It requires only one thing: an AI tool deployed across multiple teams with no access controls separating what each team can see.
When a company feeds HR records, legal contracts, financial forecasts, and sales strategy into the same AI system and gives every employee access, the AI treats all that information as a single pool of context. Ask it a question about a recent project, and it may surface compensation data from an HR thread. Ask it to summarize client activity, and it may pull in contract terms that only Legal should see.
This is not a hypothetical edge case. It is the default behavior of most general-purpose AI tools when deployed without governance architecture.
How Does Data Leak Between Departments When Using AI Tools?
Data leaks between departments through AI tools because most are designed for individual use, not organizational structure. They have no native concept of “this user is in Marketing and should not see HR data.” They process inputs and return outputs based on relevance, not permission.
Here is how it typically unfolds in practice:
- A company deploys a single AI assistant for all teams, often to boost productivity quickly.
- Various departments begin feeding the tool their own data: performance reviews, contract drafts, financial models, deal notes.
- The AI builds a shared context from all of this material.
- A user in one department asks a question. The AI, drawing on the full context pool, returns an answer that includes data from a completely different department.
- Nobody flagged it. Nobody intended it. The information is there.
The underlying mechanism is that these tools optimize for relevance, not access rights. Without an explicit permission layer, relevance always wins.
Why Is AI Data Leakage a Security Risk?
AI data leakage is a security risk because it bypasses the access controls that organizations have spent years building into their file systems, email platforms, and collaboration tools. A company may have strict folder permissions in its document management system, but if the AI tool sitting on top of that system has no equivalent controls, those permissions mean very little.
The risk compounds across several dimensions:
- Confidentiality obligations. HR data, legal communications, and financial forecasts carry professional and legal confidentiality requirements. Exposing them to unauthorized internal users can be as problematic as exposing them externally.
- Regulatory compliance. Depending on the data involved and the jurisdiction, cross-department exposure can trigger obligations under GDPR, HIPAA, SOX, or attorney-client privilege frameworks.
- Invisibility. Unlike a traditional breach, there is often no alert, log entry, or obvious moment of failure. The exposure happens quietly inside a chat window.
- Compounding over time. Every query made to an ungoverned shared AI tool is another opportunity for unintended disclosure. The risk grows with usage.
Which Departments Are Most Vulnerable to AI Data Leakage?
Four departments carry disproportionate exposure because their data is both highly sensitive and subject to formal confidentiality obligations.
Human Resources handles performance reviews, compensation structures, disciplinary records, and employee health information. This data is legally protected in most jurisdictions and operationally damaging if it reaches the wrong colleagues.
Legal manages privileged communications, contract terms, litigation strategy, and regulatory correspondence. Attorney-client privilege can be waived if privileged material is disclosed to unauthorized parties, even accidentally.
Finance works with board-level reporting, margin data, acquisition targets, and forward-looking forecasts. In publicly traded companies, premature disclosure of this material can create securities law exposure.
Sales maintains client relationship details, deal terms, competitive intelligence, and pricing strategy. This data is commercially sensitive and, in many cases, subject to non-disclosure agreements with clients.
In each case, the problem is not just embarrassment. It is a compliance and legal liability issue.
AI Data Leakage vs. Traditional Data Breaches: What Is the Difference?
A traditional data breach typically involves an external attacker, a compromised credential, or a misconfigured system that exposes data to the outside world. It is usually detectable: logs, alerts, and a clear point of failure make it easier to investigate.
Cross-department AI data leakage is structurally different in three important ways:
| Factor | Traditional Data Breach | Cross-Department AI Leakage |
|---|---|---|
| Actor | External attacker or insider threat | No bad actor required |
| Detection | Usually generates alerts or logs | Often invisible, no alert triggered |
| Scope | Data leaves the organization | Data moves within the organization |
| Cause | Security vulnerability or credential theft | Absence of access controls in AI tool |
| Compliance risk | High | High, and often overlooked |
The internal nature of AI data leakage is precisely what makes it so underestimated. Because nothing “leaves” the company in the traditional sense, many organizations do not classify it as a breach. Regulators and courts may see it differently, particularly when privileged or protected data is involved.
Can Employees Accidentally Leak Company Data Through AI Chatbots?
Yes, and it happens regularly. Employees using general-purpose AI chatbots for work tasks often paste in sensitive content without thinking through the implications: a contract clause they want summarized, a compensation table they want reformatted, a financial model they want analyzed.
When that content enters a consumer AI tool, it may be used to train future model versions, stored on third-party servers, or retained in a session that another user could theoretically access. This is the external leakage risk that most security conversations focus on.
But the internal version matters just as much. When employees use a shared company AI tool without understanding what data that tool has already ingested from other departments, they can inadvertently surface sensitive information they were never meant to see. They did not go looking for it. The AI offered it as relevant context.
For IT decision-makers, the practical implication is clear: employees need explicit guidance on what data they can and cannot enter into any AI tool, and the tools themselves need access controls that don’t rely on employee judgment alone. Pairing that guidance with strong foundational security practices reduces the overall risk surface considerably.
How to Prevent Data Leakage Across Departments with AI
Preventing cross-department AI data leakage requires both architectural decisions and policy decisions. Neither works without the other.
On the architecture side:
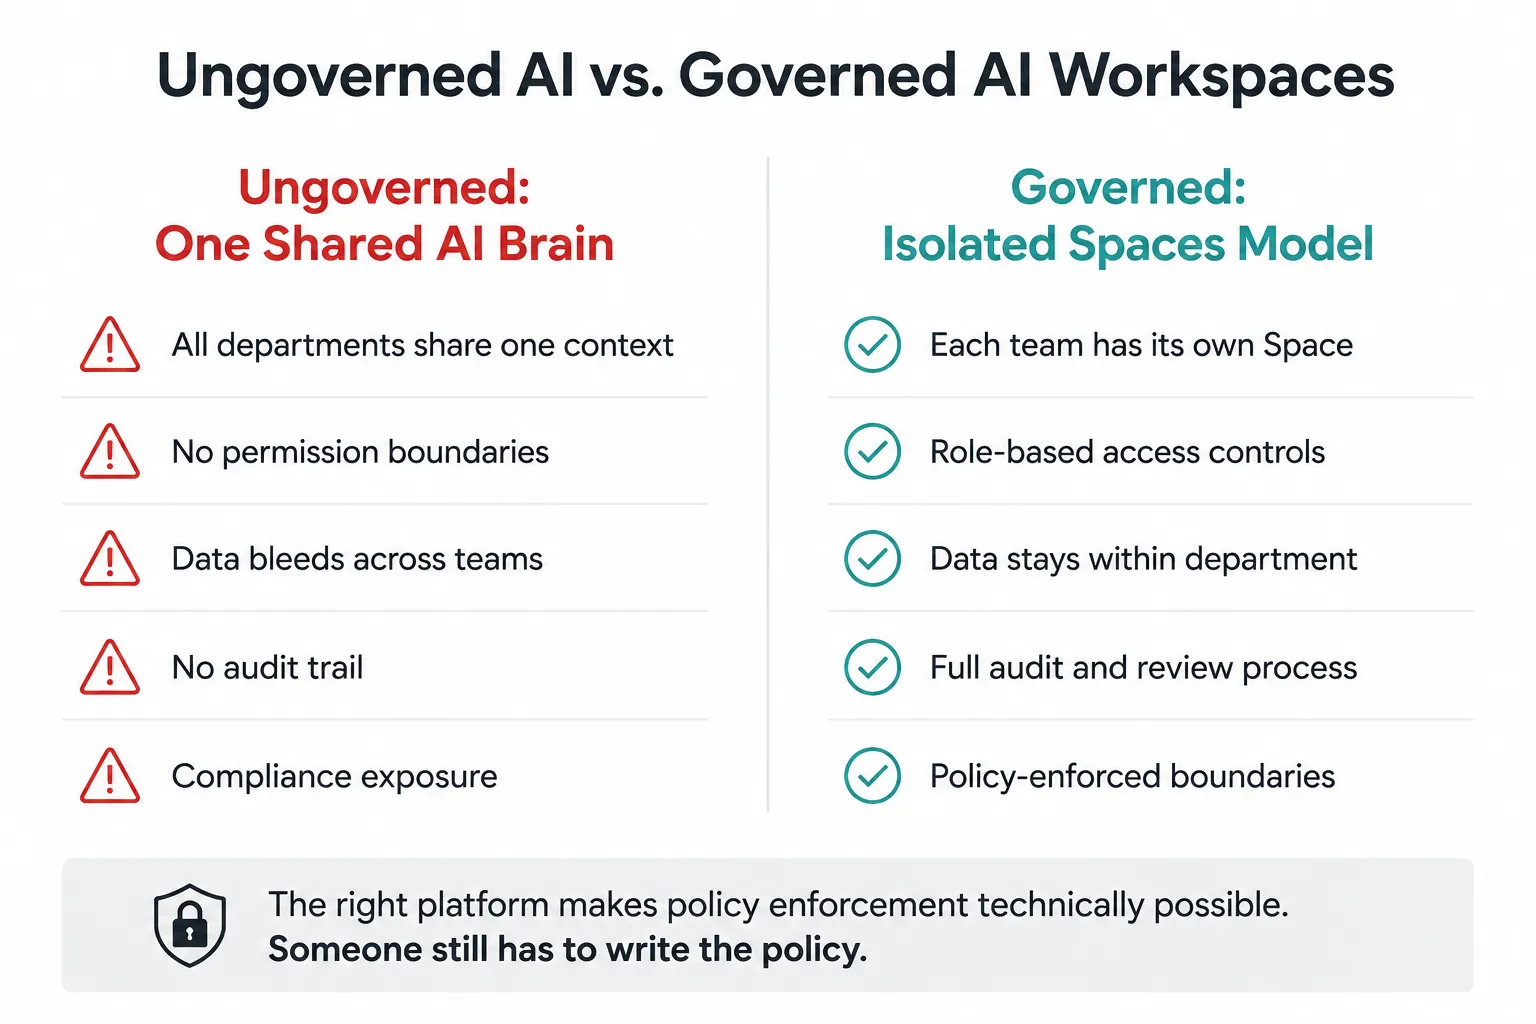
The most effective approach is deploying a governed AI platform that uses isolated workspaces, one per department or function, with role-based permissions controlling what data each workspace can access. Goodweek, for example, is built around the concept of Spaces: isolated AI workspaces configured specifically for each team. Sales gets its Space. HR gets theirs. Legal gets theirs. Each Space has its own models, data connections, and permissions. Nobody from Marketing can wander into Legal’s AI workspace. Nobody from HR can accidentally surface Finance data. The walls are built in from the start, not bolted on as an afterthought.
On the policy side:
A clear internal policy must define:
- Which teams are authorized to use AI for which tasks
- What data can and cannot be shared with an AI tool
- Who is responsible for reviewing AI usage in each department
- What the process is when a policy violation occurs
The right platform makes enforcing that policy technically possible. But someone still has to write, communicate, and own the policy.
GDPR Compliance and Cross-Department AI Data Leakage
Under GDPR, personal data must be processed lawfully, with a defined purpose and appropriate access controls. When an AI tool allows one department to inadvertently access personal data held by another (for example, HR records surfacing in a Marketing team’s AI session), that constitutes unauthorized processing of personal data.
The implications are practical and serious:
- Data subjects have rights over how their personal data is processed. Unauthorized internal disclosure can violate those rights.
- Organizations must demonstrate that access to personal data is limited to those with a legitimate need. An ungoverned shared AI tool makes that demonstration very difficult.
- Breach notification obligations may apply even for internal exposures if the data involved falls under GDPR’s protected categories (health data, financial data, etc.).
GDPR is the most commonly cited framework, but similar principles apply under HIPAA for health data, SOX for financial records, and various state-level privacy laws in the United States. For SMB leaders operating across jurisdictions, a short conversation with an IT governance partner is worth far more than a compliance audit after the fact. Understanding how data breach exposure works in practice provides useful context for why internal controls matter as much as external ones.
Common Mistakes That Cause AI Data Leakage in Companies
Most AI data leakage incidents in organizations trace back to a small set of avoidable decisions made early in the deployment process.
Deploying a single AI tool for the whole company without access controls. This is the most common mistake. Speed and convenience win out over governance, resulting in one undifferentiated AI brain that everyone can access.
Assuming the AI tool handles permissions automatically. Many IT teams assume that because their file system has folder-level permissions, the AI tool sitting on top of it inherits those permissions. Most do not. Teams must configure permissions explicitly within the AI platform.
No written policy before deployment. Rolling out an AI tool without a policy that defines authorized uses and data boundaries means employees make their own judgments, and those judgments vary widely.
Treating AI governance as a one-time setup task. Departments add new data sources, new use cases, and new users over time. Governance needs regular review, not a one-time setup.
Using consumer AI tools for sensitive work tasks. Employees who use ChatGPT, Gemini, or similar consumer tools for work documents operate entirely outside any organizational access-control framework.
Is ChatGPT Safe for Internal Company Documents?
ChatGPT and similar consumer AI tools are not designed for organizational data governance. Using them with internal company documents introduces several risks that most business owners and IT leaders underestimate.
First, data entered into consumer AI tools may be used for model training unless the user has explicitly opted out or is using an enterprise tier with contractual data protections. Second, consumer tools lack an access-control layer: anything entered into a session is visible to that session, with no organizational permission structure governing it. Third, consumer tools provide no audit trail for an IT team to review.
For tasks involving compensation data, contract terms, financial forecasts, client details, or any other sensitive category, consumer AI tools are not appropriate. Enterprise-grade platforms with explicit data governance, isolated workspaces, and contractual data protections are the right choice for business use. Exploring MacWorks 360’s AI resources provides a useful starting point for understanding what governed AI deployment looks like in practice.
How to Audit AI Usage for Data Leakage Risks
Auditing AI usage for data leakage risk is now a standard component of IT governance for any organization that has deployed AI tools across multiple teams.
A practical audit process covers five areas:
- Inventory. Identify every AI tool used across the organization, including unsanctioned consumer tools employees may use independently.
- Data mapping. For each tool, document what data it has access to, what data has been entered into it, and what data it has returned in outputs.
- Access review. Confirm that each tool’s access controls match the organization’s existing permission structure. Flag any tool that has broader access than intended.
- Policy review. Confirm that a written AI usage policy exists, that it has been communicated to all relevant staff, and that it assigns clear ownership for each department.
- Incident review. Check whether any unintended data exposures have occurred, even if they were not formally reported as incidents at the time.
For most SMBs, an IT partner who already understands the organizational structure can do this audit most efficiently. Mapping data flows across departments without that context is slow and prone to gaps.
Tools to Monitor AI Data Sharing Between Teams
Monitoring AI data sharing between teams requires tools that operate at the platform level, not just the network level. Traditional data loss prevention (DLP) tools are designed to catch data leaving the organization. They are not designed to catch data moving between departments inside a shared AI tool.
Effective monitoring for cross-department AI data leakage typically involves:
- AI platforms with built-in audit logs that record what data was accessed, by which user, in which workspace, and when.
- Role-based access reporting that flags when a user attempts to access a workspace or data source outside their assigned permissions.
- Regular review cadences where IT or a designated department owner reviews AI usage logs for anomalies.
- Endpoint monitoring to detect use of unsanctioned consumer AI tools on company devices.
The monitoring infrastructure is only as useful as the governance framework behind it. Logs without a policy defining what “normal” looks like are hard to act on.
Who Is Responsible When AI Causes Cross-Department Data Leaks?
Responsibility for cross-department AI data leakage is shared, and that shared nature makes it easy to avoid addressing it until something goes wrong.
IT leadership is responsible for selecting and configuring AI tools with appropriate access controls, maintaining audit infrastructure, and advising on platform governance.
Department heads define what data their teams use, which AI tasks are authorized within their function, and who on their team has access to which tools.
Executive leadership must treat AI governance as a business priority, not just an IT task, and allocate resources to policy development and enforcement.
The AI vendor or platform provider carries responsibility for making access controls technically available and clearly documented. A platform that does not offer isolated workspaces or role-based permissions transfers risk to the organization by design.
When an incident occurs, regulators and courts will look at all of these layers. “We didn’t know the AI was doing that” is not a defensible position when the risk was foreseeable, and the controls were available but not implemented.
What Happens If Sensitive Data Leaks Through AI Models?
The consequences of a cross-department AI data leakage incident depend on the type of data involved, the jurisdiction, and how the incident is handled.
Possible outcomes include:
- Regulatory investigation and fines if the leaked data falls under GDPR, HIPAA, or similar frameworks.
- Legal liability if attorney-client privilege is waived through unauthorized disclosure of legal communications.
- Employment law exposure if compensation or performance data reaches unauthorized employees.
- Reputational damage with clients if their confidential deal terms or relationship details surface in the wrong context.
- Internal trust breakdown between departments, which can be harder to repair than any technical problem.
Early detection and a documented response process significantly reduce these consequences. Organizations that have a clear incident response plan, including who to notify and what steps to take, are in a materially better position than those that are figuring it out in real time.
How MacWorks 360 Helps Clients Build Governed AI Environments
When MacWorks 360 helps a client deploy a governed AI platform, the engagement doesn’t end with software installation. The work includes designing the workspace structure: which departments get which access, which models fit which use cases, and what the audit and review process looks like going forward.
That means asking questions like: Should Legal’s AI workspace have access to the contract management system but not the CRM? Should HR’s workspace be completely isolated from every other department? What does a policy violation look like, and who handles it?
These are organizational questions as much as technical ones. Answering them well requires understanding how the business actually operates, not just how the software works. That is the MacWorks 360 approach: becoming a fixture in a client’s world because the goal is to know everything about it. AI governance is the newest chapter of that same story.
If you have questions about how AI is currently structured across your team, or if you’re planning a deployment and haven’t fully addressed governance, a short conversation now is worth far more than an incident investigation later.
macworks360.com | 973-671-1122
Frequently Asked Questions
What is cross-department AI data leakage?
Cross-department AI data leakage is the unintended exposure of one department’s sensitive data to another department’s users through a shared AI tool that lacks access controls. No malicious action is required. The AI surfaces whatever it has been fed, regardless of who is asking.
How is this different from a normal data breach?
A traditional breach typically involves an external attacker or a compromised credential, and it usually generates a detectable alert. Cross-department AI leakage is internal, often invisible, and produces no alert. It can happen dozens of times before anyone notices.
Which departments face the highest risk?
HR, Legal, Finance, and Sales carry the most exposure because their data comes with formal confidentiality obligations. Unauthorized disclosure can trigger regulatory, legal, and employment law consequences.
Can this happen with tools like ChatGPT?
Yes. Consumer AI tools lack an organizational access-control layer. Data entered into them is outside any company permission structure. Enterprise-grade platforms with isolated workspaces and contractual data protections are the appropriate choice for sensitive business use.
Is cross-department AI data leakage a GDPR violation?
It can be if personal data is processed by or disclosed to someone without a legitimate purpose and legal basis under GDPR; that constitutes unauthorized processing, regardless of whether the disclosure was intentional. Specific outcomes depend on the data involved and the circumstances.
What is the fastest way to reduce this risk?
The fastest meaningful step is to stop using a single shared AI tool with no access controls and move to a platform that supports isolated workspaces and role-based permissions. Pair that with a written policy that defines authorized uses and data boundaries.
Do AI platforms automatically inherit file system permissions?
Most do not. You must configure permissions explicitly within the AI platform. Assuming that existing folder-level permissions carry over to an AI tool is one of the most common and consequential mistakes in AI deployment.
Who is responsible when AI causes a cross-department data leak?
Responsibility is shared across IT leadership, department heads, executive leadership, and the AI platform vendor. Regulators will look at all of these layers. “We didn’t know” is not a defensible position when the risk was foreseeable, and controls were available.
How often should AI usage be audited?
At minimum, quarterly. More frequently during the first year of deployment, when data sources and use cases are still being established. Any significant change in how a department uses AI (new data connections, new users, new tasks) should trigger a targeted review.
What should an AI usage policy include?
At minimum: which teams are authorized to use AI for which tasks, what data can and cannot be shared with an AI tool, who is responsible for AI usage in each department, and what happens when a policy is violated.
Is this risk only relevant to large enterprises?
No. SMBs are often more exposed because they are more likely to deploy AI tools quickly without a formal governance process. The data involved (employee records, client contracts, financial forecasts) is just as sensitive in a 50-person company as in a 5,000-person one.
What does a governed AI workspace look like in practice?
A governed AI workspace gives each department an isolated environment with its own data connections, model configuration, and permission settings. Users in one department cannot access or inadvertently surface data from another department’s workspace. Audit logs track all activity for review.
Published by MacWorks 360 | AI Security and Governance | August 2026